Enterprise Security & Tenant Isolation Built for Independent Commercial Brokerages
Built from the database layer up to protect policyholder Nonpublic Information (NPI). Our platform enforces dual-layer agency isolation, zero AI model training on your policies, and alignment with state and federal insurance data privacy requirements.
The Six Pillars of Insure Assist AI Platform Trust
Architected to protect commercial policy data and support your agency's compliance obligations under state insurance regulations and the GLBA Safeguards Rule.
Dual-Layer Multi-Tenant Isolation
Brokerage data is separated by hardware-enforced relational database rules. Every transaction binds to your unique agency ID, making cross-tenant data access mathematically impossible.
- check_circlePostgreSQL FORCE ROW LEVEL SECURITY on all tenant tables
- check_circleCryptographically decoded JWT token verification on every API route
- check_circleMandatory brokerId filters at application code and database layer
- check_circleZero cross-tenant data leakage or shared prompt contexts
Cloud Infrastructure & Cryptography
All compute and database storage reside exclusively in Google Cloud Platform US data centers (us-central1). Data is shielded with state-of-the-art encryption in transit and at rest.
- check_circleEnforced TLS 1.3 encryption with HTTP Strict Transport Security (HSTS)
- check_circleHardware-accelerated AES-256 disk and cloud storage object encryption
- check_circleCloudflare Enterprise edge WAF and automated DDoS protection
- check_circleZero non-US data transit or off-shore hosting dependencies
Enterprise AI Privacy & Zero-Retention
Your policy declarations, schedules, and client PII are never fed into public foundation models. Ingestion and extraction occur via stateless private enterprise API endpoints.
- check_circleZero model training guarantee: Customer data never trains public LLMs
- check_circlePrivate enterprise Google Vertex AI infrastructure with enterprise data protection
- check_circleStateless document parsing with ephemeral inference memory destruction
- check_circleAgency retains 100% intellectual property and data ownership
Identity Governance & Access Control
Rigorous access controls ensure team members only access authorized operational functions, backed by Multi-Factor Authentication (MFA) and cryptographic session management.
- check_circleMulti-Factor Authentication (MFA) enforcement across all agency accounts
- check_circleGranular Role-Based Access Control (Admins, Producers, CSRs, Auditors)
- check_circleSeparation of administrative privileges from daily certificate issuance
- check_circleTime-limited cryptographic session tokens with automatic timeout
Business Continuity & Cloud Resilience
Engineered for continuous commercial brokerage operations with automated replication, multi-zone failover capabilities, and regular snapshot protection.
- check_circleAutomated daily multi-zone database snapshots with point-in-time recovery
- check_circleContainerized microservices running on Google Cloud Run with multi-zone redundancy
- check_circleGeo-redundant Google Cloud Storage for policy documents and certificates
- check_circleZero single points of failure in core document processing pipelines
Regulatory Due Diligence Support
Technical controls and data governance specifically designed to assist independent brokerages in meeting their statutory third-party service provider due diligence obligations.
- check_circleDesigned to support agency compliance with NY DFS 23 NYCRR 500 § 500.11
- check_circleSupports NAIC Insurance Data Security Model Law (#668 § 4) vendor oversight
- check_circleContractual safeguards aligned with FTC / GLBA Safeguards Rule (16 CFR Part 314.4)
- check_circleDirect engineering security support available for agency compliance reviews
Dual-Layer Tenant Isolation & Cryptographic Boundaries
Unlike generic SaaS applications that rely solely on software code to separate customer accounts, Insure Assist AI pairs application-level Broken Object Level Authorization (BOLA) with hardware-enforced PostgreSQL kernel Row-Level Security (RLS).
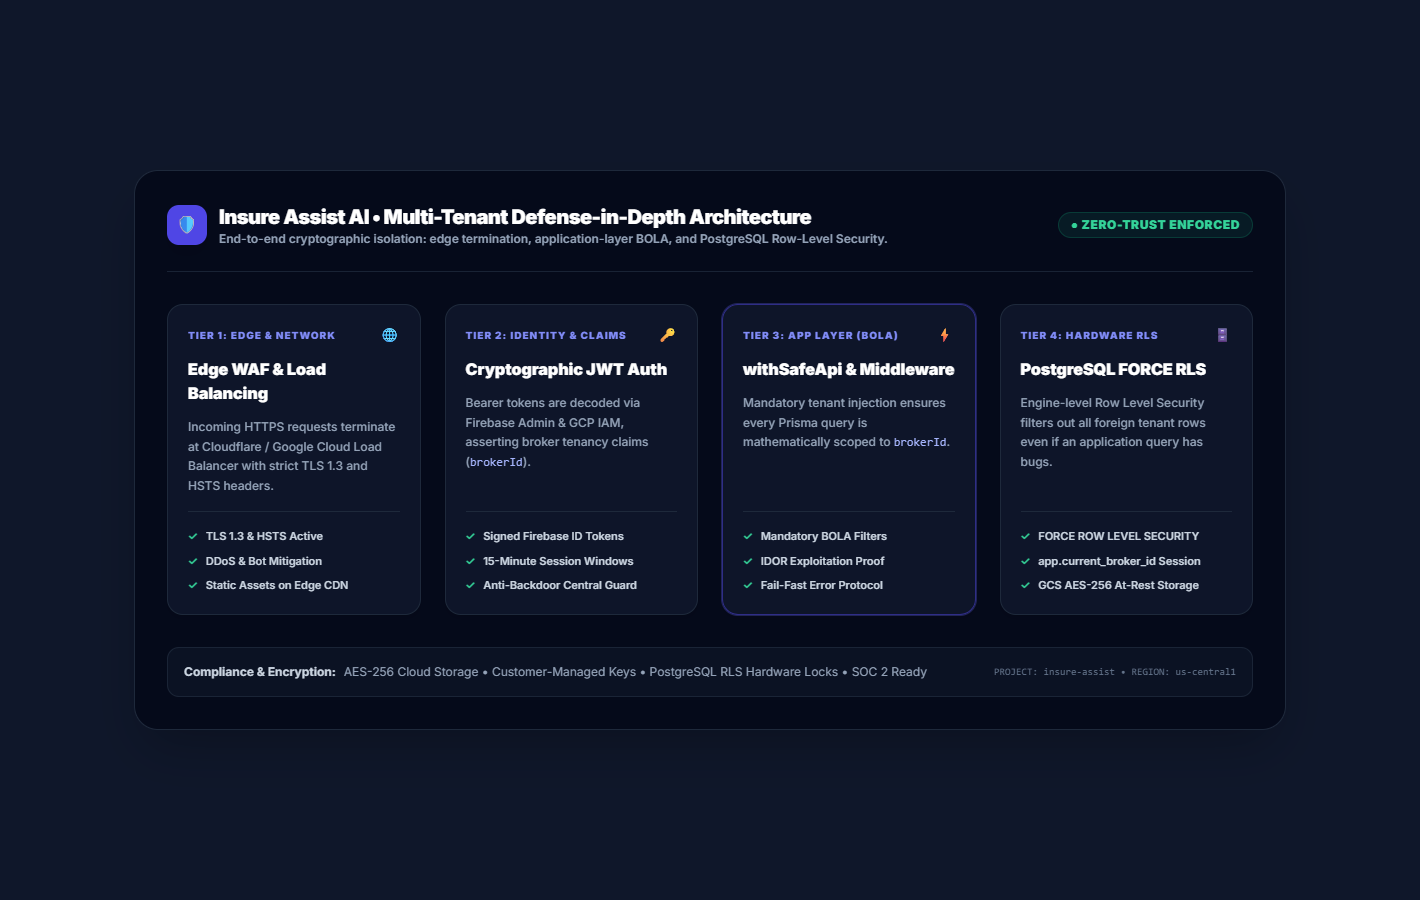
Every incoming API request cryptographically decodes verified session claims signed by Google Cloud identity services. Database queries strictly inject the authenticated brokerId, rejecting unauthorized cross-tenant requests.
Before executing any SQL query, database connections set a session config variable matching the active agency identity. PostgreSQL enforces FORCE ROW LEVEL SECURITY, guaranteeing that even a compromised application query cannot read rows from another agency.
Policy OCR and document extraction execute in ephemeral container memory over private Google Cloud Vertex AI connections. No customer policy texts, dec sheets, or FEINs are stored in shared AI caches or used to train public foundation models.
Have Questions About Your Agency's Compliance Review?
Agency principals, compliance officers, and IT committees often require structured documentation to satisfy state due diligence requirements (such as NY DFS 23 NYCRR 500 § 500.11, NAIC Model 668 § 4, and the GLBA Safeguards Rule). Our engineering security desk assists qualified brokerages directly with questionnaires, architectural specifications, and data protection agreements.
Standard Information Gathering (SIG Lite) responses covering hosting, encryption keys, access governance, and recovery protocols.
Detailed technical breakdown of PostgreSQL Row-Level Security, BOLA prevention, and stateless Vertex AI inference boundaries.
Ready-to-sign Data Processing Addendum confirming 100% agency data ownership and guaranteed 30-day post-termination data wipe.
[email protected]Frequently Asked Security Questions
Key questions asked by commercial agency owners and risk managers before onboarding.
Never. Insure Assist AI operates under a strict Zero-Model-Training policy. Your commercial policy uploads, loss runs, ACORD forms, FEINs, and commercial driver schedules are processed over private enterprise Google Cloud Vertex AI endpoints and are never used to train, retrain, or improve public or foundation artificial intelligence models.